Pass the audit, answer the board, win the tender.
Without a security team.
Built by a CISO with 25 years in the chair, for teams that don't have one. Audit-ready for every regulation your customers and auditors ask about, including NIS2, GDPR, ISO 27001 and DORA, with the assessments, controls, policies and reporting your auditor expects, all in one platform. Free baseline in 15 minutes.
Built in Ireland, under EU rules. Used by teams anywhere, from SMEs to multinationals.
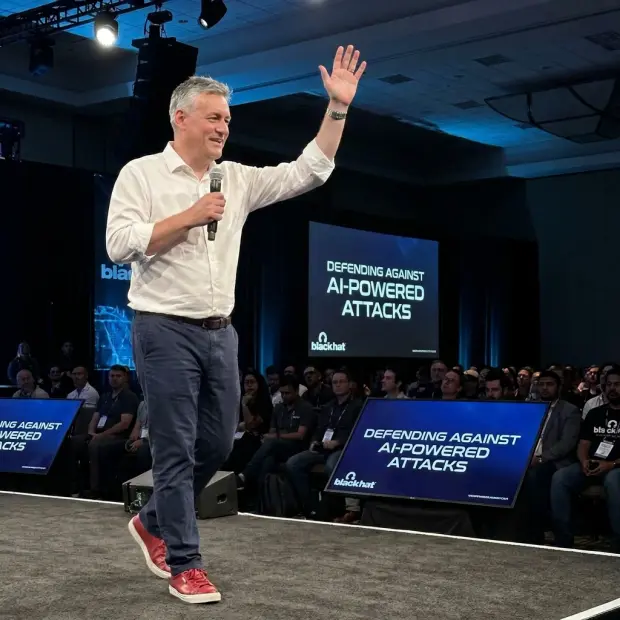 On stage at Black Hat
Dr Matt Lemon
Founder & CISO
I didn't design ShieldIQ from a feature list. I built it from 25 years in the CISO chair, steering organisations through live ransomware attacks, EU data-sovereignty fights, and regulators at the door.
But the idea came from the ground up. Working hands-on with SMEs, I kept seeing the same thing: the tooling built for big enterprises didn't fit them, and the gaps left them exposed. ShieldIQ grew directly out of that, shaped by the real problems those teams face, not built in a lab.
Everything else I've learned is in it too. I hold a PhD in Digital Security & Forensics, wrote the cybersecurity books others now train from (Applied Cybersecurity and Applied AI Security), founded the Global CISO Council in Ireland, and speak regularly at industry conferences. Today I also teach the next generation as an Associate Professor of Cybersecurity.
ShieldIQ is all of it: every framework, every hard lesson, every 3am incident, turned into software a smaller team can actually run. Enterprise-grade security leadership, without the enterprise price tag.
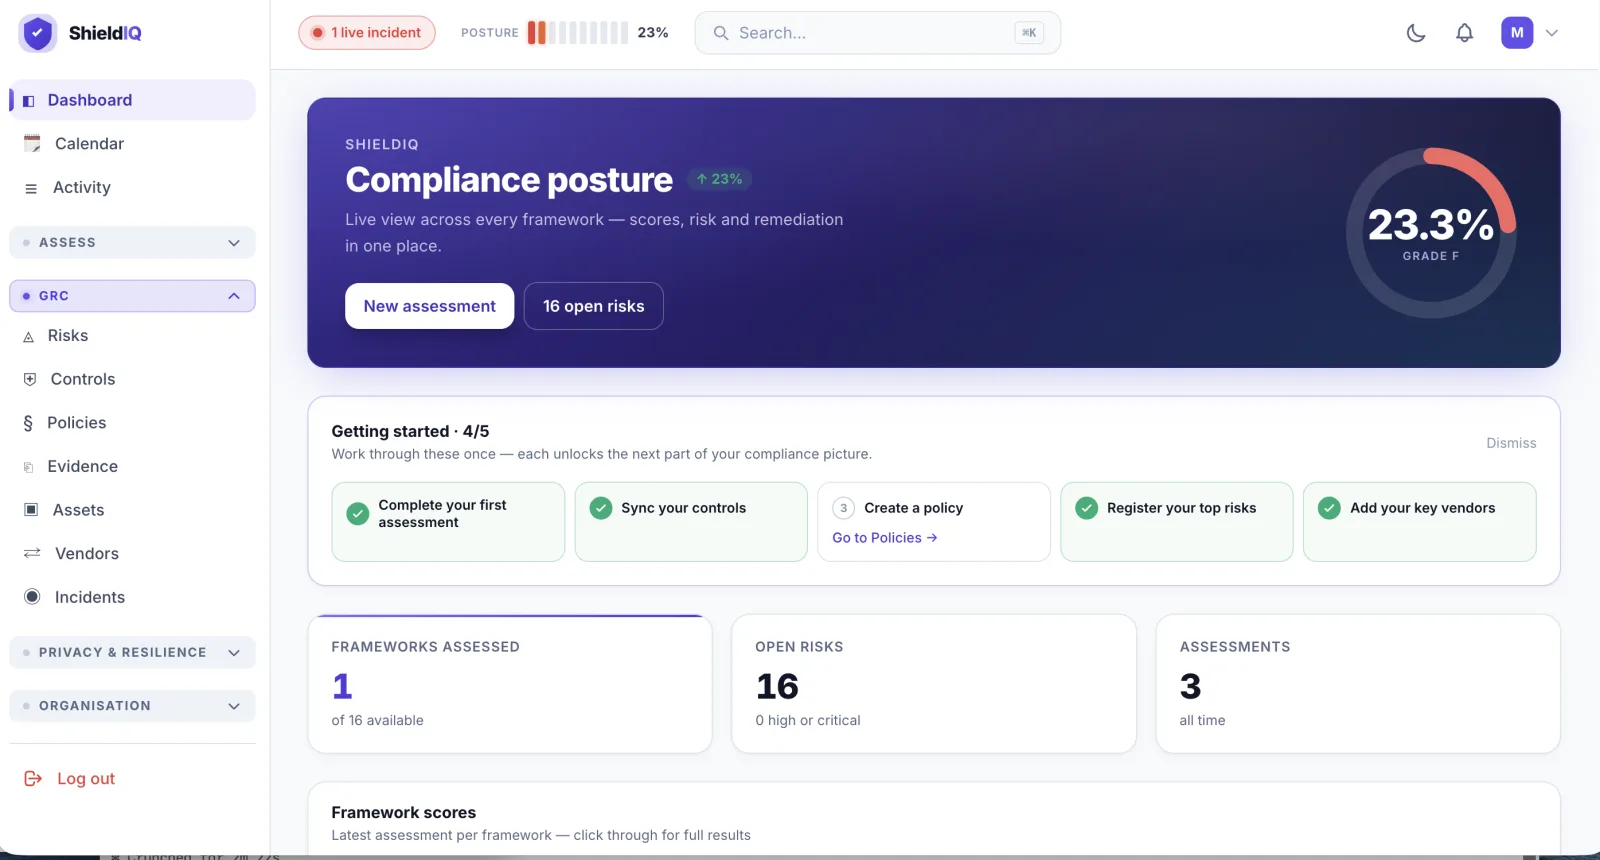
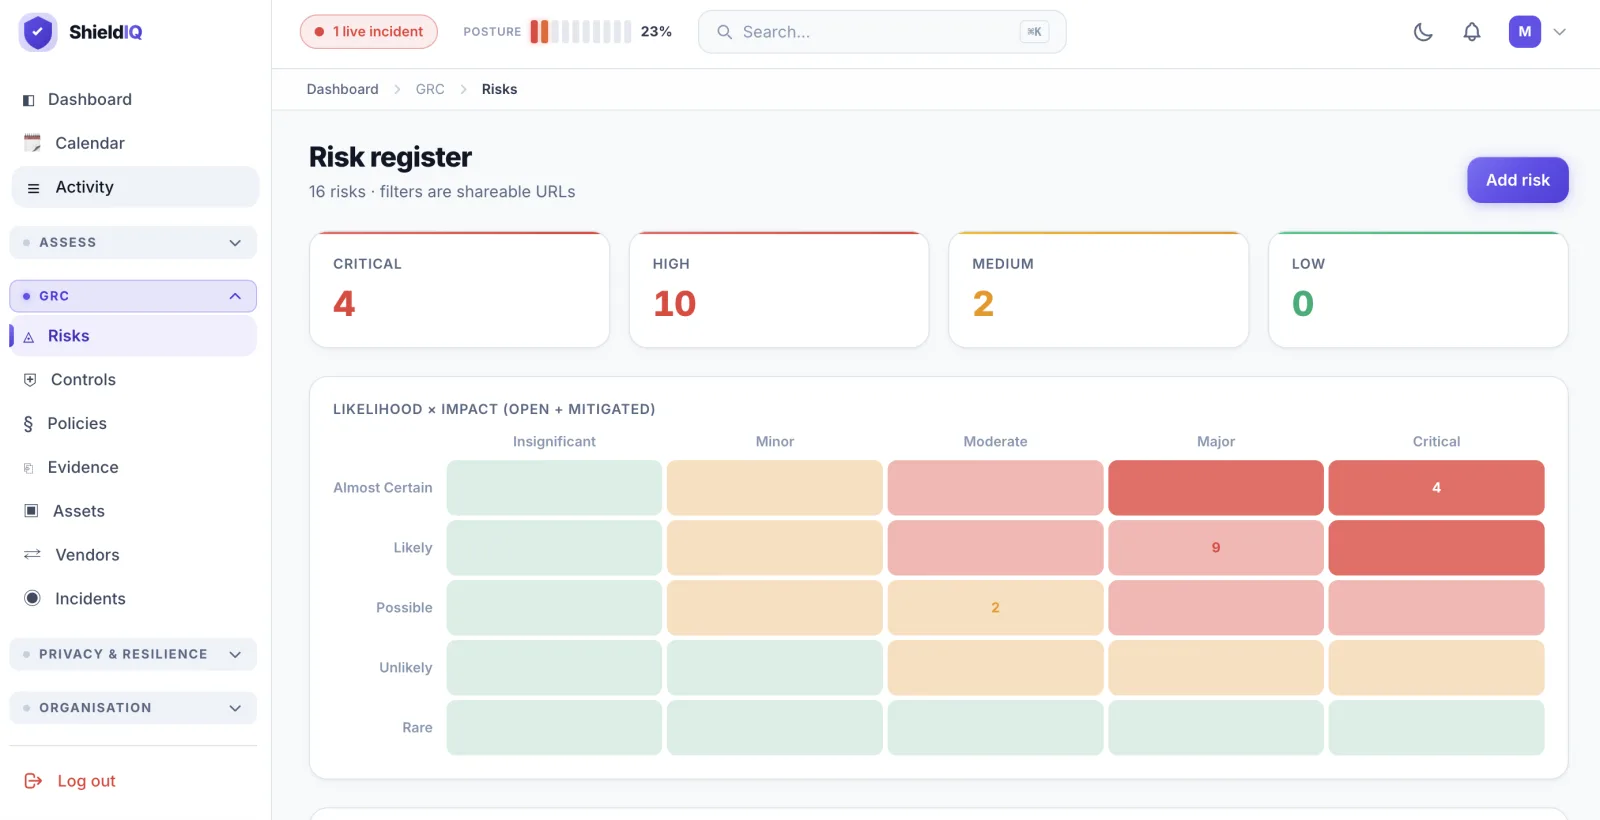
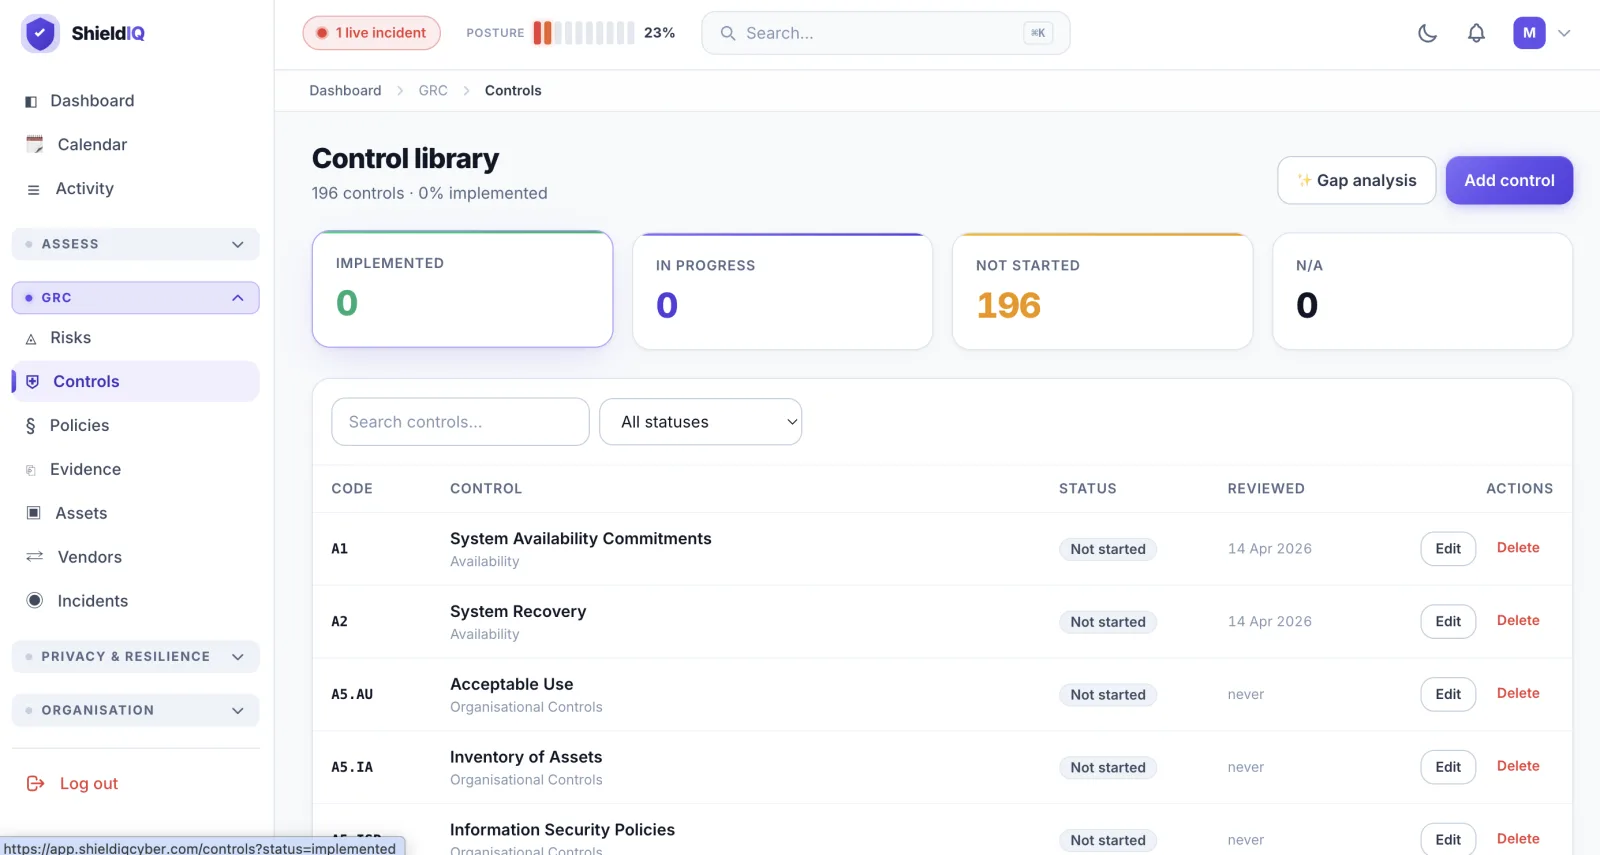
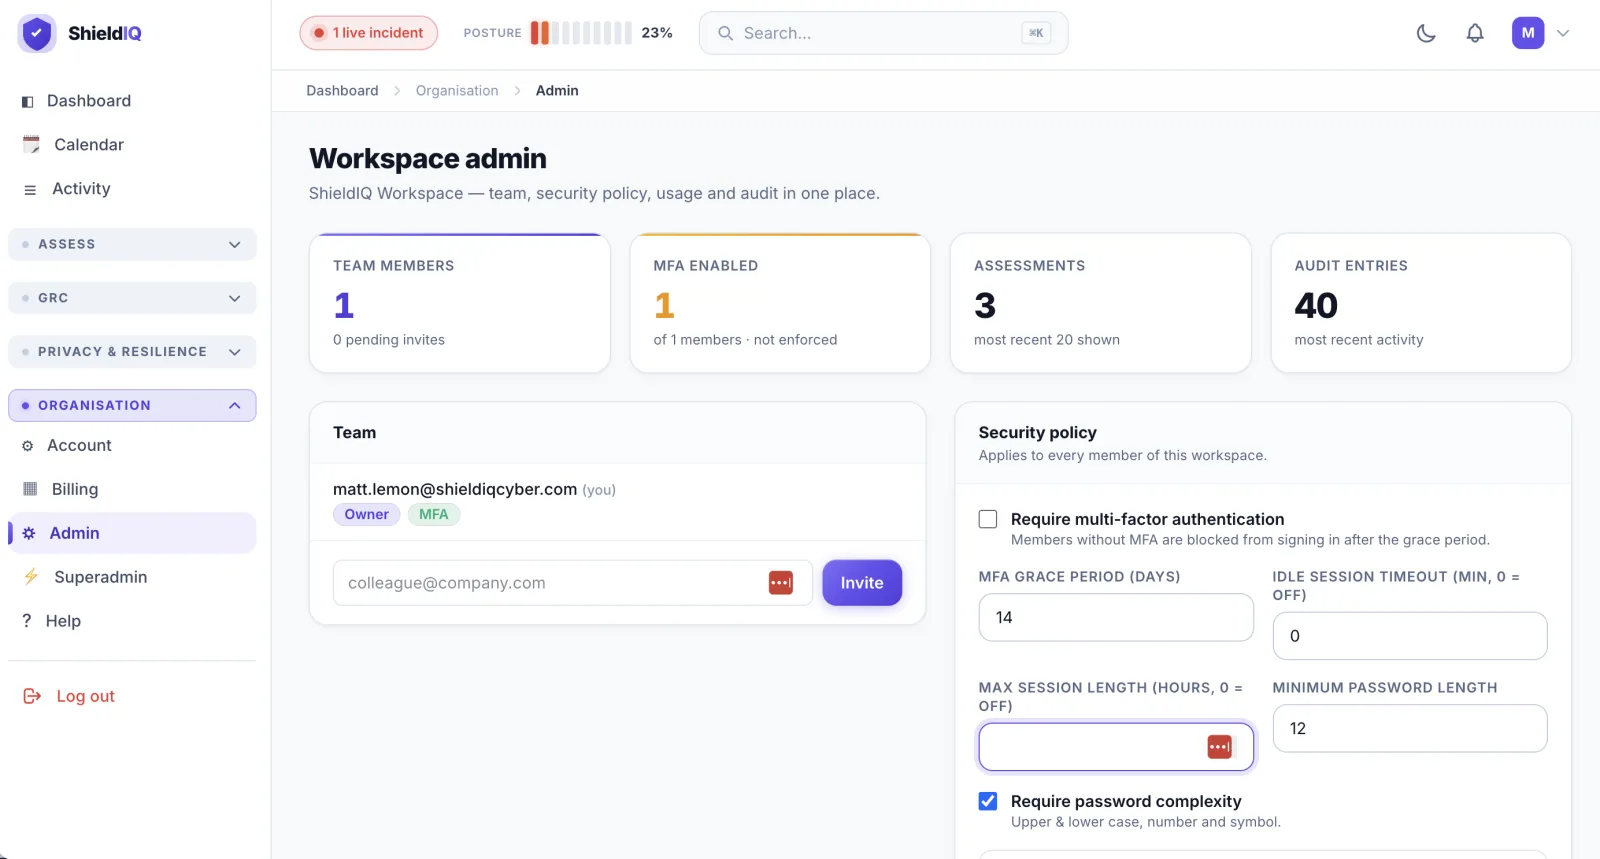
We have secured teams at
Consulting Services
Prefer hands-on support?
The platform does the heavy lifting, but sometimes you want an expert alongside you. ShieldIQ's Dublin-based consultants work as an extension of your team, from a one-off assessment to an ongoing programme, led by a CISO who has been in your seat.
Regulations keep multiplying.
Your headcount doesn't.
Each new regulation brings its own deadlines, evidence requirements and penalties. But you don't have a security team, and consultants charge a fortune for a report that's out of date the day they walk out the door.
Where the deadlines stand
GDPR · DORA · PCI DSS 4.0
Already applies. Penalties are live.
NIS2 · EU AI Act (high-risk)
Landing now, hard deadlines through 2026.
EU AI Act (2027) · more to come
Plan ahead so it isn't a scramble.
ISO 27001, NIST CSF, SOC 2 and Cyber Essentials are voluntary standards, adopt them when you're ready.
ShieldIQ gives you a way to get compliant, and stay compliant, without either.
Why you need this now
Three things that will cost you
if you wait.
Your customers are asking
Security questionnaires, and NIS2 and DORA supply-chain clauses, are arriving in supplier contracts. Banks, insurers, utilities and public bodies have to manage the security risk of the firms they buy from, so they pass the questions down to you.
No evidence means a stalled deal, or a lost one.
If you sell to regulated companies →The regulator is coming
NIS2 fines reach €10m or 2% of worldwide turnover for essential entities, and €7m or 1.4% for important entities. Management bodies can be held personally liable (NIS2 Art. 20). DORA already applies to EU financial entities, and reaches their ICT suppliers through their contracts.
The board signs off on cyber risk, and answers for it.
What NIS2 means for you →The old way is slow and expensive
A one-off consultant report typically costs €10,000 or more, and is out of date the day they leave. A virtual CISO retainer typically runs €3,600 to €5,500 a month.
Most SMEs can't justify either, so nothing gets done.
Compare the cost →Your next big customer will send a security questionnaire. Be ready to answer it.
Find out where you stand today, for free, in about 15 minutes.
Get my free baselineHow it works
Audit-ready in three steps
No setup calls, no professional services. Start in minutes.
Start free, today
Create a free account, pick the framework your customer or regulator is asking about, and begin. No credit card, no sales call.
Know exactly what to fix first
In around 15 minutes of guided questions you get every category scored, your gaps named, and a prioritised plan to close them.
Walk into the board meeting, or the audit, with proof.
Your controls, risks, policies and incidents live in one place, so the board-ready report and the auditor's evidence are ready when you are.
Early users
What early users say.
Having a CISO with 25 years of experience available without the full-time cost is exactly what we needed. ShieldIQ gave us a clear picture of our compliance posture within the first week.
NIS2 compliance felt impossible until we started using ShieldIQ. The gap analysis and AI policy drafting saved us weeks of work.
Every framework you're asked for
Answer whichever framework they ask for.
Built for the rules EU firms actually face: NIS2, DORA, GDPR, the EU AI Act, the Cyber Resilience Act and CyFun, alongside ISO 27001, SOC 2 and NIST CSF 2.0. Built in the EU, ready for whichever market you sell into.
The NIST Cybersecurity Framework (CSF 2.0) is free to assess. All other frameworks are available on a paid plan.
4 outcomes · one platform
Everything you need. Nothing you don't.
Every module is grouped by the job it gets done: pass the audit, answer customer questionnaires, report to the board, and handle an incident on the clock.
Pass the audit
9 modulesScored assessments, mapped controls, versioned policies and a tamper-evident trail your auditor can check for themselves.
Answer customer questionnaires
6 modulesWhen a customer sends a security questionnaire, the answers and the evidence are already in one place.
Report to the board
4 modulesShow the board where you stand, what it costs if it goes wrong, and who is fixing what by when.
Handle an incident on the clock
2 modulesThe 24-hour, 72-hour and 4-hour regulator clocks start themselves, and the notification is drafted for you.
24h early warning. 72h notification. 4h DORA initial report. ShieldIQ starts the clock for you.
NIS2: tell the national authority within 24 hours of becoming aware of a significant incident.
NIS2 incident notification, and the GDPR deadline for reporting a personal-data breach to the DPC.
Financial entities: within 4 hours of classifying an ICT incident as major.
Log the incident and the deadlines that apply to you start running, with the regulator notification drafted for you to review. Included from the Professional plan up.
AI-Powered
Your AI compliance analyst, built in.
ShieldIQ's AI reads your assessment in your business context, drafts policies you can edit, judges whether your evidence actually proves a control, finds the gaps, and drafts your incident notifications. It's the expertise of a GRC consultant, without the day rate. All on one shared credit pool, no surprise bills.
AI Assessment Analysis
A consultant-grade read-out you can hand straight to your MD. Each category is analysed in your business context, 2 to 3 paragraphs per category, in every assessment.
AI Policy Drafter
Your full policy set in an afternoon, not a five-day consultancy job. Pick a policy type, scope and framework, then review, edit and save each tailored draft.
AI Evidence Judge
Know before your auditor does whether your evidence will pass. Upload a file and get a verdict (satisfies, partial or does not satisfy) with reasoning and fixes.
AI Incident Notifications
Never miss a regulator's deadline. Drafts regulator-ready notifications with the correct GDPR, NIS2 and DORA clocks already running.
AI Gap Analysis
Know exactly what to fix first. Finds gaps across your controls and frameworks, ranks the remediation, and keeps you audit-ready between audits.
A CISO, not a chatbot
The AI does the heavy lifting. A 25-year CISO designed the method.
The AI reads your answers, drafts your policies and checks your evidence, so work that used to take a consultant weeks takes an afternoon. What it checks you against was designed by Dr Matt Lemon: 25+ years as a CISO, CISSP, CISM, CISA and ISO 27001 Lead Auditor, who as CISO at Huawei Mobile Services achieved ISO 27001, 27017, 27018, 27701 and CSA STAR.
You know who is behind the method, and you can talk to him.
- Every planAI analysis that follows a CISO's method, in your business context.
- Consulting PilotYour evidence is reviewed by a senior CISO before it goes to an auditor or a customer.
- EnterpriseA one-hour CISO review call every other month, on top of the platform.
Compare
Three ways to get compliant
Know what it costs, start the same day, and get a method built for the rules you actually face.
| Question | Security consultancy | Typical compliance platform | ShieldIQ |
|---|---|---|---|
| Price shown upfront | No, quoted per engagement | Usually quote-only | Yes, from €99 / month |
| Start free without a sales call | No | Usually demo first | Yes, free NIST CSF 2.0 baseline |
| Time to first result | Weeks | After an onboarding call | About 15 minutes |
| Built for EU rules (NIS2, DORA, CRA, CyFun) | Depends on the firm | Varies, often SOC 2 first | Yes, all four built in |
| Named CISO behind it | Usually, at day rates | Typically an unnamed team | Yes, Dr Matt Lemon |
| Breach-notification clocks built in | Templates, not live clocks | Varies | Yes, 24h / 72h / 4h |
Platform column based on publicly available pricing pages, October 2026; consultancy column reflects typical engagements in Ireland. Breach clocks are included from the Professional plan up.
Pricing
Start for free. Scale when ready.
Price on the page. No demo required.
No credit card required to get started. Your first assessment takes around 15 minutes.
The NIST Cybersecurity Framework (CSF 2.0) is free to assess. All other frameworks are available on a paid plan.
Starter
Always free. No card required.
For anyone asked 'are we secure?' who wants an honest answer before spending a cent. Achieve: a scored NIST CSF baseline and your biggest gaps, in 15 minutes.
- 1 framework (NIST CSF 2.0)
- 1 assessment / quarter
- AI assessment analysis included
- Risk register: 10 risks · 10 assets
- 1 quick scan / month
- 1 user · community support
Professional
or €2,739 / year (12 months for the price of 11)
For a small team taking on NIS2, ISO 27001 or GDPR properly. Achieve: a shared programme with policies at scale, and incidents handled inside the regulator's clock.
- Any 3 frameworks
- 6 assessments / quarter
- 500 risks · 500 assets · 25 policies
- 75 AI credits / month
- Incident management (24h / 72h / 4h clocks) · 20 AI incident drafts / month
- Standard scans · 10 quick scans / month
- CSV + email reports
- 5 users · email support (48h)
Also available: Individual at €99 / month, Business at €449 / month and Enterprise at €1,200 / month (inc VAT). Compare every plan
FAQ
Frequently asked questions
What is a GRC platform?
GRC stands for governance, risk and compliance. A GRC platform brings those three together in one place, so instead of juggling spreadsheets for assessments, controls, policies, risks, vendors and incidents, you run them from a single system that stays audit-ready. ShieldIQ is a GRC platform built specifically for smaller teams.
Do I need to comply with NIS2?
If you operate in the EU in a sector NIS2 covers, such as energy, health, digital infrastructure, transport, manufacturing and many others, and you are a medium or large entity, you very likely fall in scope. Even where you are not directly regulated, your customers and supply chain increasingly expect NIS2-level security. ShieldIQ helps you assess your obligations and close the gaps.
How long does a compliance assessment take?
Your first baseline takes about 15 minutes. You work through a guided assessment, and ShieldIQ scores you against the framework, shows your gaps and prioritises what to fix first. A full programme takes longer, but you get a clear picture of where you stand on day one.
What frameworks does ShieldIQ support?
Seventeen, including NIS2, GDPR, ISO 27001, DORA, the EU AI Act, NIST CSF 2.0, SOC 2, PCI DSS and Cyber Essentials. NIST CSF 2.0 is free to assess and the rest are on a paid plan. Every framework has scoring, gap analysis and prioritised remediation built in.
Is ShieldIQ suitable for SMEs without a dedicated security team?
Yes, that is exactly who it is built for. Most small and mid-sized businesses cannot justify a full-time compliance team, so ShieldIQ gives you the assessments, controls, policies and reporting a security lead would produce, guided by AI and structured so a non-specialist can run it. If you want an expert alongside you, our consultants can step in too.
How much does ShieldIQ cost?
You can start for free, with no card required. The free Starter plan includes a full NIST CSF 2.0 assessment with AI analysis and a risk register for up to 10 risks and 10 assets. Paid plans are Individual at €99 a month, Professional at €249, Business at €449 and Enterprise at €1,200 (inc VAT). Pay annually and get 12 months for the price of 11. See the pricing page for exactly what each plan includes.
Where is my data stored?
Your data is hosted in the EU (Ireland) on AWS. Security and privacy are the whole point of the product, so tenant isolation, encryption and audit logging are applied by default. AI analysis and drafting is processed by Anthropic (Claude) in the US, which does not train on your data.
Can I get hands-on help, not just the software?
Yes. Alongside the platform, our Dublin-based consultants work as an extension of your team, from a one-off assessment to an ongoing programme, covering virtual CISO, GRC programmes, strategic planning and incident response. The software and the human expertise are designed to work together.
See your compliance posture in 15 minutes,
and leave with a prioritised plan.
Free to start. No credit card. No setup calls. Your first NIST CSF 2.0 baseline is free, and every other framework is a click away on a paid plan.